Code Audit Services
Find what could make your codebase unsafe to keep building on.
Get a senior-led Codebase & Production Readiness Audit for $499, with a detailed report within 7 days after scope and required access are confirmed. For AI-built, inherited, outsourced, or existing software. We investigate the codebase, validate meaningful findings, and tell you what should happen next.
Six engineering review areas
Validated findings with severity and priority
Detailed remediation direction
Fixes scoped separately
$499 · Full audit · Detailed report · Delivered within 7 days*
*Delivery begins after scope and required access are confirmed.
When an Audit Becomes Useful
Your app works. The codebase may still be carrying risk.
Use an audit when the next product decision depends on knowing what is actually happening inside the system.
Built fast with AI
The app works, but you do not know whether security, architecture, testing, or deployment shortcuts will hold up under real use.
Inherited codebase
A freelancer, agency, previous team, or former developer built the system. Your current team needs evidence before it keeps investing in it.
Development keeps getting harder
Changes are slower, regressions are more common, or simple features now touch too many parts of the system.
Someone says rebuild
Before replacing working software, you want evidence showing what is actually wrong and whether targeted remediation is more sensible.
What We Review
We review the codebase through six engineering lenses.
The emphasis changes with your product, stage, stack, and the reason for the audit.
Code Quality & Maintainability
We look for complexity, duplication, coupling, inconsistent patterns, and other conditions that make safe change harder or more expensive.
Architecture
We evaluate boundaries, responsibilities, data flow, coupling, scalability constraints, and the blast radius of future changes.
Security & Data Handling
We review authentication, authorization, sensitive-data handling, secrets, input handling, and other security-sensitive implementation risks.
Testing & Reliability
We assess whether critical product behavior can be verified reliably after meaningful changes, not simply how many tests exist.
Dependencies & Technical Risk
We review vulnerability signals, support status, version gaps, compatibility, upgrade pressure, and external-service dependency risk.
Deployment & Production Readiness
We review deployment, environments, observability, backups, recovery, rollback, and other controls that affect reliable operation.
Product requirements, test material, architecture documentation, workflows, acceptance criteria, and other relevant context are also reviewed where available to establish expected behavior and verification confidence.
How the Audit Works
From product context to an engineering decision.
We move from context and access to validated findings, priorities, and a practical next step.

Understand the system
We start with the product, architecture, current stage, and the concern that triggered the audit. Available requirements, workflows, test material, and architecture documentation help establish expected behavior.

Set up audit access
We obtain the repositories, environments, and technical context required for the agreed audit scope. Access requirements are confirmed before the audit begins. How we handle repositories, credentials, and ownership is documented on Security, IP & Engineering Standards.

Inspect the implementation
Engineers review the agreed audit areas across the codebase and supporting engineering environment, using documentation where it helps explain expected behavior.

Validate the findings
Tools, checklists, documentation, and engineering review can surface signals. We investigate them in context before treating them as audit findings.

Prioritize what matters
Validated findings keep credible source classifications where applicable, use category-specific engineering severity where needed, and receive remediation priority.

Recommend the next move
The report helps you decide whether to keep building, harden, refactor, rescue, or investigate rebuilding.
Scanners find signals. Engineers validate what actually matters.
Source signal → Engineering investigation → Validated finding → Severity & remediation priority → Recommended action. A Senior Engineering Lead owns the technical judgment while the Project Manager keeps the review connected to product context, scope, and the question that triggered the audit.
Inside Our Engineering Review
See the evidence engineers use to investigate risk.
These examples come from our internal production-readiness assessment process and show some of the controls and engineering signals we inspect during a review.
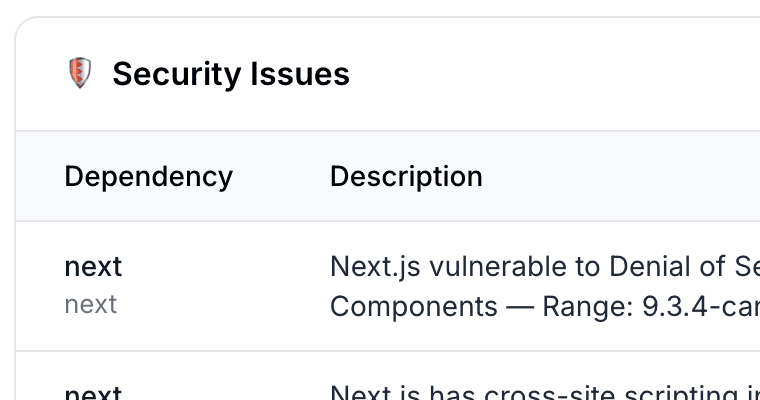
Security & access controls
Review authentication, authorization, secrets, session behavior, and security-sensitive data access.
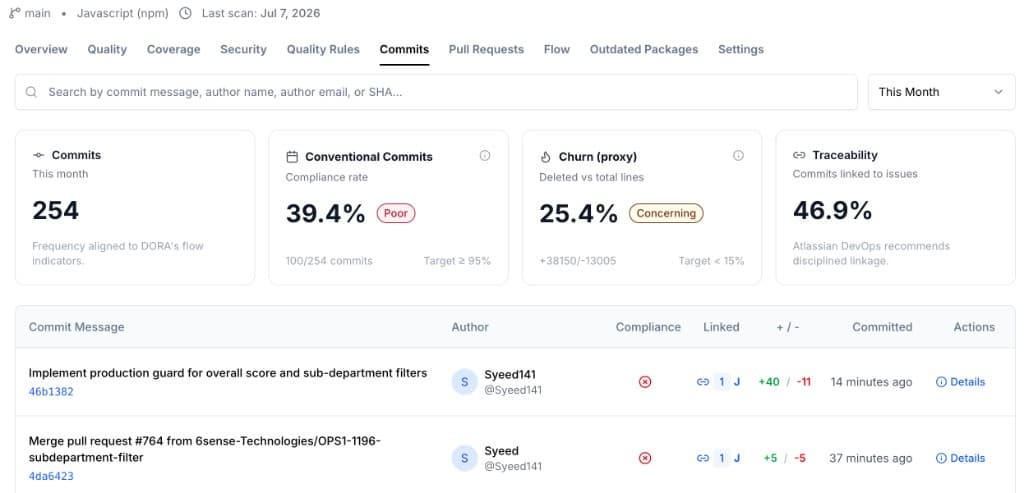
Engineering workflow & traceability
Review change activity, code churn, issue traceability, and engineering signals that can reveal delivery and maintainability risk.
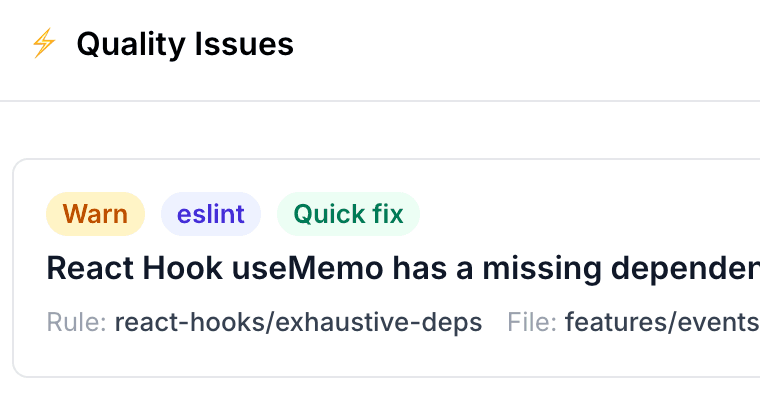
Code, testing & maintainability
Review whether the codebase can be changed, verified, operated, and maintained with reasonable confidence.
These examples demonstrate our assessment methodology and internal review criteria. They are not client outcomes or fabricated findings.
Real Audit Finding
See how a signal becomes an engineering decision.
A finding should explain more than what a tool detected. It should show what engineers investigated, what was confirmed, why it matters, and what should happen next.
| Finding format | 6sense Codebase Audit |
|---|---|
| Finding | A High Next.js advisory sits on the framework that serves production traffic |
| Context | Dependencies / web framework · next |
| Source classification | Npm audit / advisory signal — High — Next.js Denial of Service with Server Components — GHSA-mwv6-3258-q52c — Package: next — Direct dependency |
| Engineering severity | High — the App Router path is live in production |
| Remediation priority | Before next milestone |
| Evidence / investigation | Our dependency review surfaced a High advisory on next for Denial of Service with Server Components (GHSA-mwv6-3258-q52c). The package is installed directly and powers the production App Router, so this is not unused leftover software. Engineering confirmed the affected framework is on the live request path before treating the advisory as a material finding. |
| Why it matters | A reachable DoS condition on the framework that serves customer traffic can interrupt product availability. Leaving a confirmed High advisory on an active production dependency increases the chance of avoidable outage risk before the next release window. |
| Recommended action | Upgrade next to a patched release listed in GHSA-mwv6-3258-q52c, redeploy the application, and rescan dependencies to confirm the advisory is cleared. Keep the item before the next milestone unless production exposure is confirmed sooner. |
Finding
- 6sense Codebase Audit
- A High Next.js advisory sits on the framework that serves production traffic
Context
- 6sense Codebase Audit
- Dependencies / web framework · next
Source classification
- 6sense Codebase Audit
- Npm audit / advisory signal — High — Next.js Denial of Service with Server Components — GHSA-mwv6-3258-q52c — Package: next — Direct dependency
Engineering severity
- 6sense Codebase Audit
- High — the App Router path is live in production
Remediation priority
- 6sense Codebase Audit
- Before next milestone
Evidence / investigation
- 6sense Codebase Audit
- Our dependency review surfaced a High advisory on next for Denial of Service with Server Components (GHSA-mwv6-3258-q52c). The package is installed directly and powers the production App Router, so this is not unused leftover software. Engineering confirmed the affected framework is on the live request path before treating the advisory as a material finding.
Why it matters
- 6sense Codebase Audit
- A reachable DoS condition on the framework that serves customer traffic can interrupt product availability. Leaving a confirmed High advisory on an active production dependency increases the chance of avoidable outage risk before the next release window.
Recommended action
- 6sense Codebase Audit
- Upgrade next to a patched release listed in GHSA-mwv6-3258-q52c, redeploy the application, and rescan dependencies to confirm the advisory is cleared. Keep the item before the next milestone unless production exposure is confirmed sooner.
Sanitized internal audit finding. Product-identifying details have been removed. This is not a client result.
What You Actually Get
You receive a detailed audit report, not a scanner dump.
Detailed Audit Report
A documented engineering assessment of the agreed review scope, validated findings, supporting context, risks, and recommendations.
Prioritized Findings
Material findings include severity or source classification, remediation priority, why the issue matters, and the recommended response.
Remediation & Hardening Direction
See what should happen immediately, before the next milestone, as planned work, or be consciously accepted and monitored.
Engineering Decision
Evidence to support Keep Building, Harden, Refactor, Rescue, or Investigate Rebuilding.
Scope & Price
A full $499 audit. Remediation is separate.
We confirm the application scope before payment. Standard audits are delivered within 7 days after scope and required access are confirmed.
$499 full audit
Covers one application within the agreed standard scope and includes the detailed engineering report.
Delivered within 7 days
The delivery clock starts after the agreed scope and required access are confirmed.
Scope confirmed before payment
If your system requires a larger or more complex review, we tell you before payment and confirm a custom scope.
No fixes included
The audit diagnoses, validates, prioritizes, and recommends. Any implementation is a separate engagement.
No payment is required before the standard audit scope has been confirmed.
How Findings Are Classified
Severity tells you how serious it is. Priority tells you when to act.
We preserve credible source classifications and use category-specific engineering rules where tools are not enough.
| Classification | How it is applied |
|---|---|
| Source Classification | Credible source classifications remain visible. |
| Engineering Assessment | Category-specific engineering rules apply when tools are not enough. |
| Strategic Gaps | Important engineering capability gaps remain separate from severity. |
| Remediation Priority | Immediate · Before Next Milestone · Planned · Accept & Monitor. |
Source Classification
- How it is applied
- Credible source classifications remain visible.
Engineering Assessment
- How it is applied
- Category-specific engineering rules apply when tools are not enough.
Strategic Gaps
- How it is applied
- Important engineering capability gaps remain separate from severity.
Remediation Priority
- How it is applied
- Immediate · Before Next Milestone · Planned · Accept & Monitor.
Source Signal → Engineering Investigation → Validated Finding → Severity → Remediation Priority → Recommended Action
Detailed severity rules
Category-specific engineering rules for how we classify findings.
Who Reviews Your Codebase
Senior engineering judgment owns the audit.
A Senior Engineering Lead and Project Manager oversee the audit, with relevant specialists supporting deeper investigation where needed.
Senior Engineering Lead
Owns the technical assessment, validation of findings, severity, remediation priority, and final engineering recommendations.
Project Manager
Establishes product context, coordinates scope and access, and keeps findings connected to the question that triggered the audit.
Backend, frontend, cloud/DevOps, security-sensitive implementation, and database/infrastructure specialists may support deeper investigation. The buyer receives one consolidated audit—not disconnected specialist reports.
What Happens After the Audit
The report tells you what to do next. The next engagement is optional.
The audit may support continuing as-is, targeted hardening, deeper rescue work, or investigating a rebuild.
Keep Building
Continue normal development when the foundation is reasonable.
Production Hardening Sprint · $6K–$15K
Address contained production blockers and high-priority findings.
- Learn more
Software Project Rescue · $15K–$60K+
For substantial stabilization, remediation, or architecture work.
Investigate Rebuilding
Only where evidence shows replacing significant parts makes more sense.
- Learn more
Production Engineering Pod · $5K–$12K+/month
Ongoing engineering ownership after stabilization.
The audit does not exist to manufacture remediation work. Diagnosis comes first.
Not Sure You Need the Audit?
Check your situation for free first.
The Production Readiness Check helps determine whether your situation appears to justify code-level engineering investigation. This is not a free code audit.
Questions before you start a code audit
Scope, timing, access, deliverables, and what happens after the report.
Know what is wrong before you invest more in the codebase.
Start the $499 Codebase & Production Readiness Audit and get a detailed report within 7 days after scope and required access are confirmed.